// service
API Development
We design and build REST and GraphQL APIs that are secure, well-documented and ready to handle real traffic. Our backend engineers have built production APIs powering fintech apps, marketplaces, healthcare platforms and SaaS products — with proper authentication, rate limiting, caching and monitoring built in from day one. We also handle complex third-party integrations: payment processors, CRMs, messaging platforms, AI APIs, and more.
// sound familiar?
Is This the Right Fit?
// who it's for
Built For These Situations
// what's included
What You Get
// outcomes
What Success Looks Like
// why codexcelerate
Why Clients Choose Us
Security-first backend engineering
We follow OWASP API Security Top 10 on every project — input validation, parameterized queries, rate limiting, secure token storage, and least-privilege access control. Security isn't an audit item; it's how we write backend code.
Integrations that don't break
We build third-party integrations with idempotency, retry logic, webhook signature verification and dead-letter queues. When a vendor's API goes down or changes, your system degrades gracefully rather than crashing.
Documentation you actually use
We generate OpenAPI/Swagger docs from code so they never drift out of sync. New engineers, mobile clients and partner integrations can understand your API without reverse-engineering request logs.
Designed for your future, not just today
We version APIs from day one, use database migrations not manual SQL, and structure code so your next engineer can extend it without being afraid to touch it. Clean code isn't a luxury — it's cheaper long-term.
// comparison
Us vs. a Typical Agency
| What we compare | CodeXcelerate | Typical agency |
|---|---|---|
| Documentation | OpenAPI/Swagger auto-generated | Often a Notion doc that drifts |
| Error handling | Retry logic, dead-letter queues | Try/catch and hope |
| Security | OWASP Top 10 addressed by default | Security done at audit time |
| Test coverage | Unit + integration tests | Often manual-only |
// tech we use
Our Toolkit
// process
How We Deliver
Discovery
We map your goals, users and constraints into a clear product brief and fixed scope.
Design
We design the experience and architecture before a line of code ships.
Build
We build in agile sprints with weekly demos and full transparency into progress.
Launch
We ship to production with testing, monitoring and a smooth rollout plan.
Support
We stay on as your team — iterating, optimizing and scaling with you.
// client reviews
What Clients Say
"CodeXcelerate took TradeBeep from just an idea to a launched product — the app, the admin panel, the landing page, and even our marketing. Having one team handle the build and the growth made everything seamless."
Oluwole Kayode
Founder, TradeBeep
"They built Snap To Let end to end, from concept to launch, and the quality was excellent. We trusted them so much that we're now building a second product with them."
Geetha Nath
Founder, Snap To Let
// related work
Related Case Studies
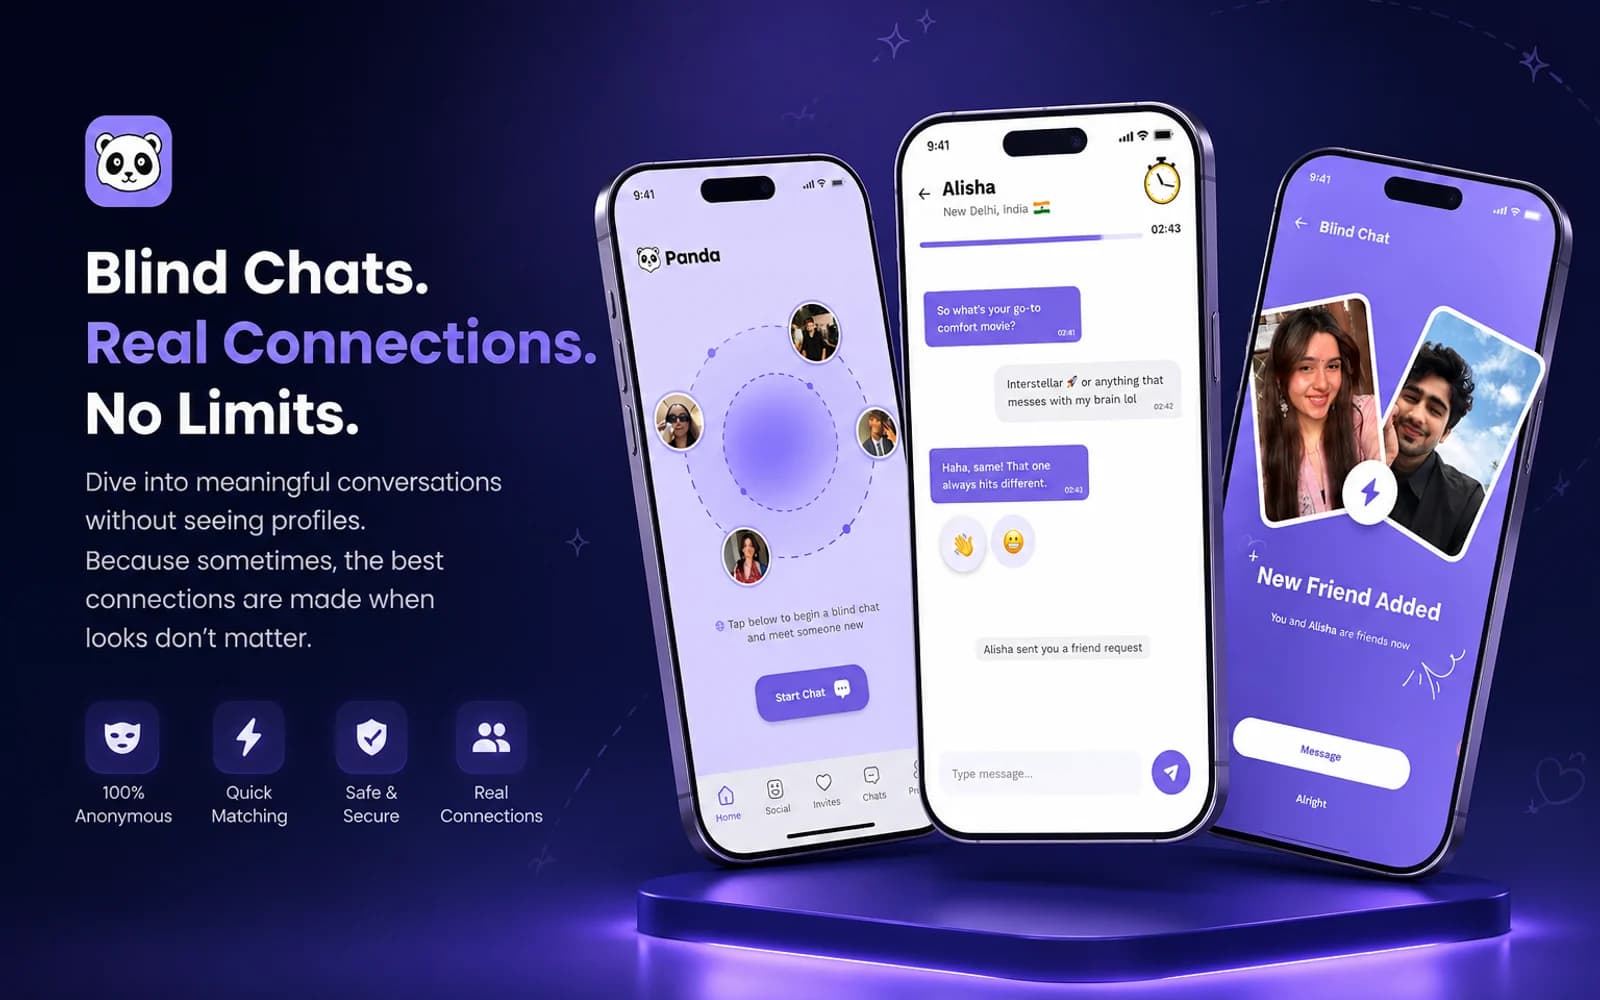
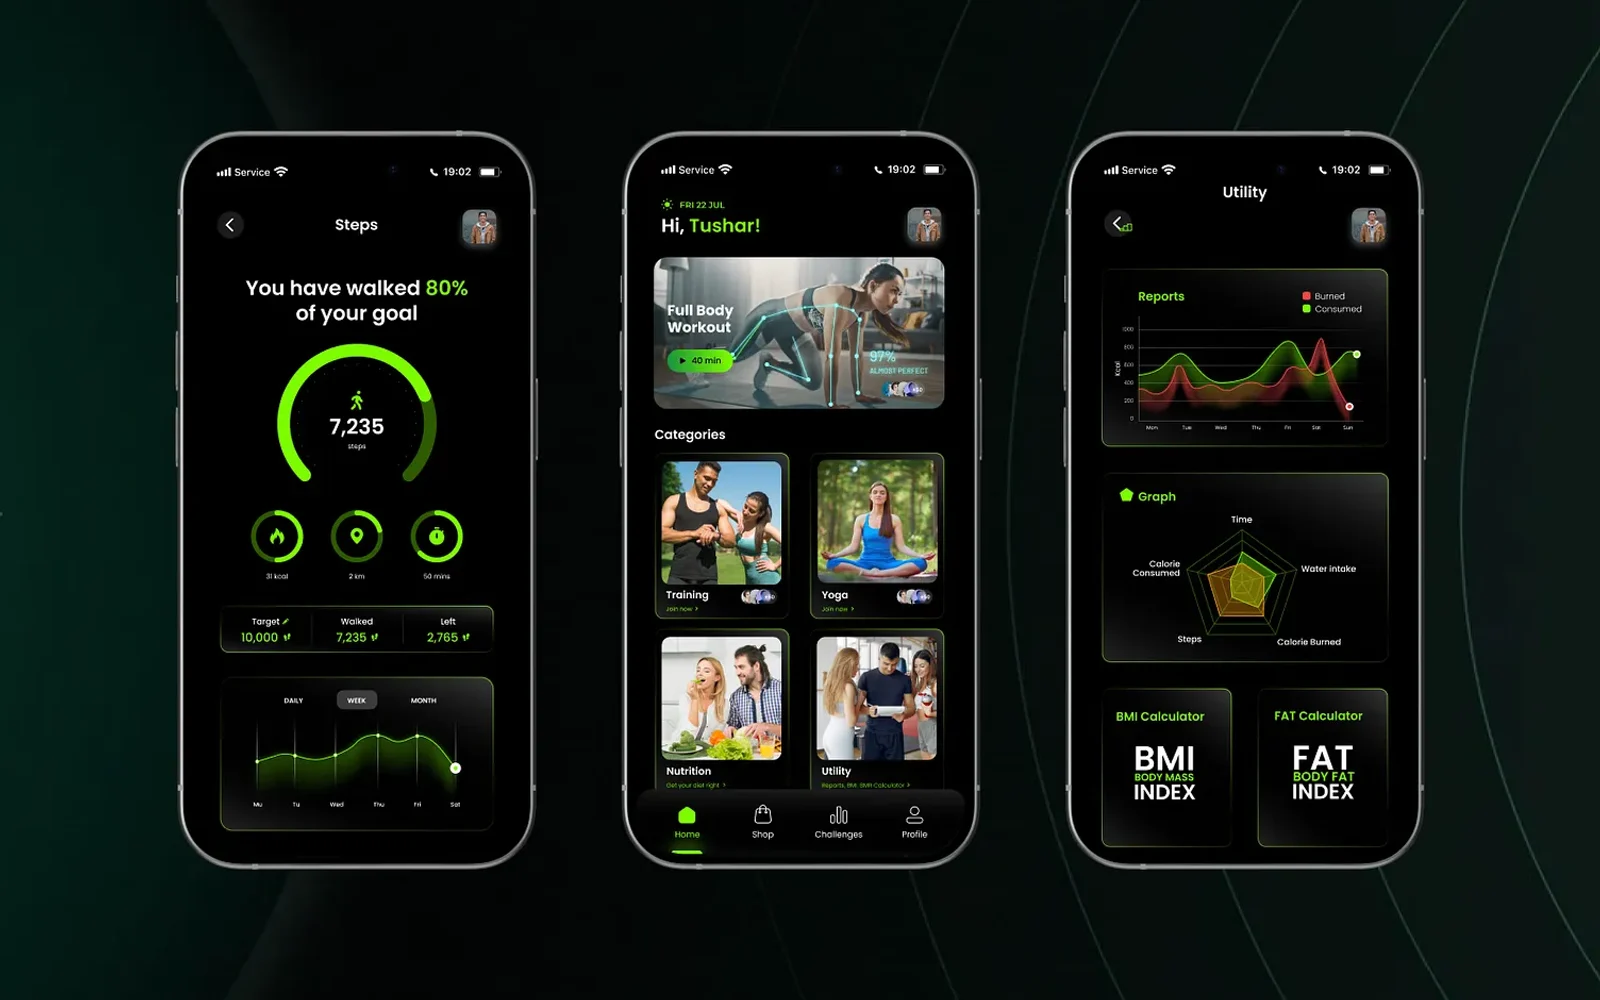
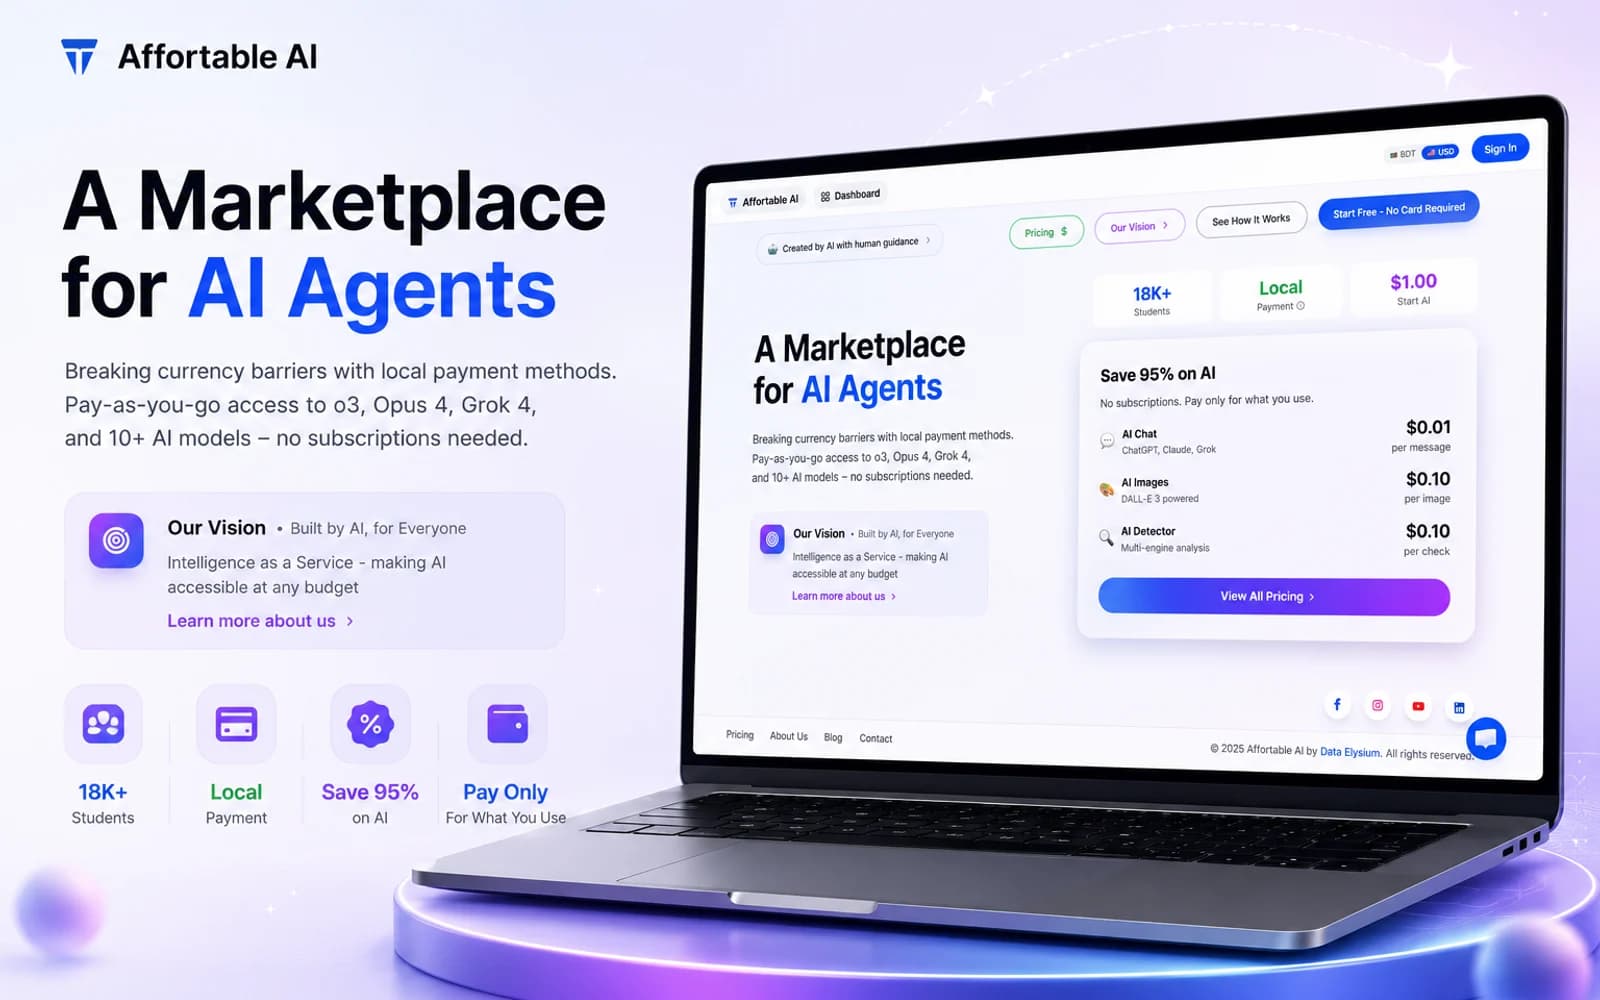
// faq
Frequently Asked Questions
Both. We recommend REST for simple, cacheable resources and public APIs where predictability matters. We recommend GraphQL for complex UIs that need to fetch precise, nested data from multiple resources. We'll help you choose the right approach for your specific product during discovery.
Let's build it together
Tell us what you're building and get a free, no-obligation quote — we reply within 4 hours.